01
Cloud and identity
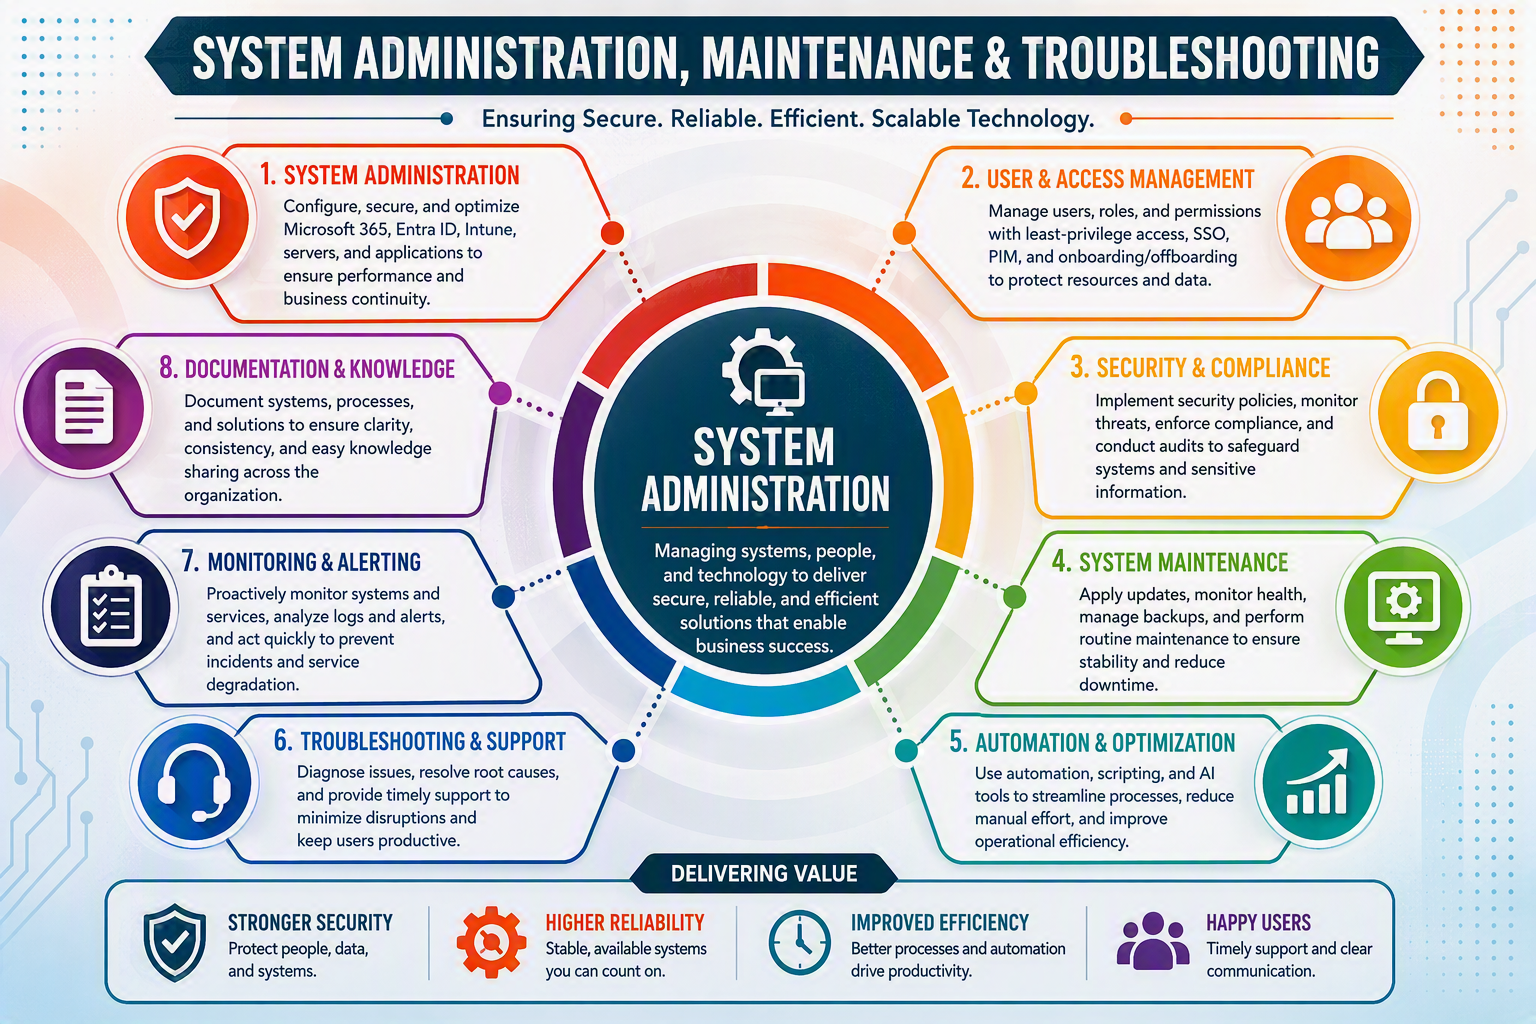
Administer Microsoft 365 and Microsoft Entra ID services, including licensing, role-based access, Conditional Access, authentication methods, SSO, access reviews, and Privileged Identity Management.
Systems Administration · Security Operations
I build and maintain dependable Microsoft environments by connecting thoughtful administration, disciplined security practices, and automation that makes day-to-day operations more resilient.
info@mitchellstewart.caOperating focus
Identity and access control
Endpoint security and compliance
Detection, response, and recovery
Technical scope
Strong administration is a balance: services must be available and usable while identities, devices, data, and changes remain controlled.
Administer Microsoft 365 and Microsoft Entra ID services, including licensing, role-based access, Conditional Access, authentication methods, SSO, access reviews, and Privileged Identity Management.
Manage Windows endpoints with Microsoft Intune, including configuration, compliance, application deployment, patching, remediation, and device lifecycle support.
Investigate security alerts, suspicious email, endpoint vulnerabilities, and SIEM incidents across Defender for Endpoint, Defender for Office 365, Defender XDR, and Microsoft Sentinel.
Keep enterprise applications and services supportable through monitoring, documentation, change coordination, vendor management, and practical automation.
Security focus
Security is part of the operating rhythm: protect access, maintain healthy devices, notice unusual activity, and make the response repeatable.
Representative work
The goal is not only to keep systems running, but to make the environment easier to protect, understand, and improve.
Managed Microsoft 365, Entra ID, Exchange Online, Conditional Access, authentication methods, SSO integrations, and privileged access controls across the organization.
Administered Intune configuration, compliance, application deployment, and remediation policies while monitoring patching and operational health for 800+ managed devices.
Administered Defender XDR, Defender for Office 365, and Sentinel SIEM; investigated alerts and incidents, applied mitigations, and coordinated escalation when needed.
Developed incident-response plans, administered phishing simulations and security training, and supported Purview data loss prevention policies to strengthen security awareness.
Role experience
Maintained the cloud services, identities, permissions, and access controls that people rely on every day.
Supported a consistent, secure endpoint experience through policy, deployment, patching, and operational health management.
Connected security operations with automation and documentation so recurring work could be handled consistently and at scale.